Tech nuts, bolts, and cyber jolts—your place for insider tips.
September 15, 2026
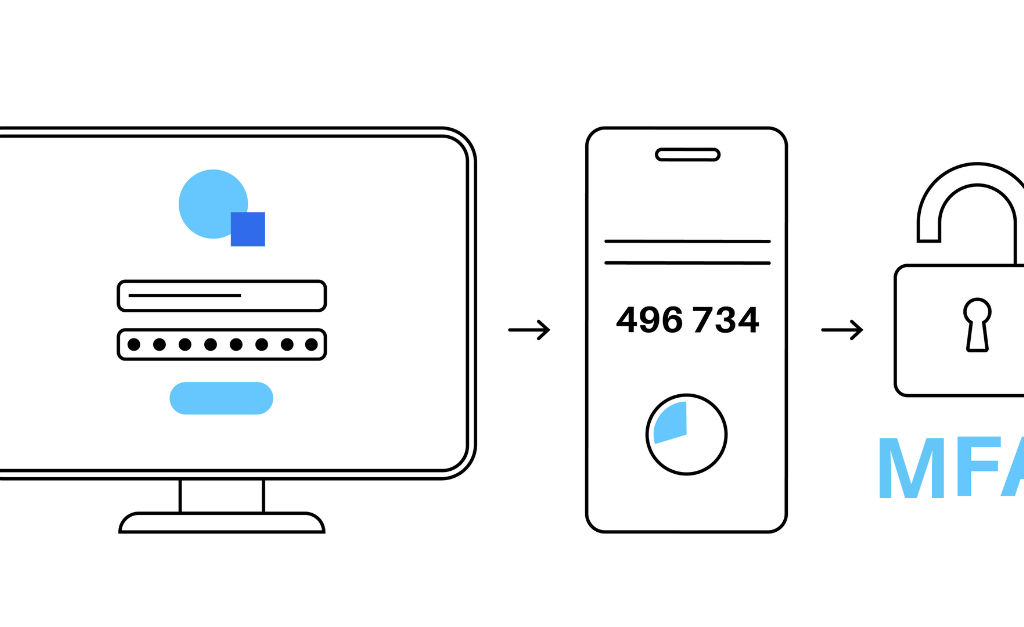
What is MFA and why everyone needs it Awooga, awooga—all aboard! MFA stands for Multi-factor Authentication, and if you’re not already on this security train, it’s high time you hop...
September 10, 2026
What is small business cybersecurity? Small business cybersecurity is the mix of habits, tools, and training that protect your company’s data, money, and systems from attackers. For most small and...
August 5, 2026
Prevent Business Interruptions Before They Happen—No Time Machine Required Ever dream of hopping into your DeLorean for a little time travel? Just imagine the possibilities—undoing embarrassing moments, remembering to back...
August 4, 2026
The short version: most cyber hacks aren’t personal — criminals hunt for easy openings, not specific victims. Here are three types of hacks most businesses don’t expect: supply chain attacks...
July 1, 2026
What is cybersecurity training? Cybersecurity training teaches your team to recognize and stop the everyday threats—phishing emails, fake invoices, vishing calls, social engineering—behind most data breaches. The 9 types below...
June 3, 2026
What is phishing? Phishing is a cyberattack where criminals impersonate a trusted person or organization—via email, text, phone, or even physical mail—to steal passwords, financial information, or access to your...
We use cookies to enhance your experience, analyze site traffic, and provide personalized content. By continuing to use this website, you agree to our use of cookies.