What is small business cybersecurity? Small business cybersecurity is the mix of habits, tools, and training that protect your company’s data, money, and systems from attackers. For most small and mid-sized businesses, the biggest risks aren’t elaborate hacking schemes carried out by the hooded figures you see in movies. They’re phishing emails, weak or reused passwords, and team members who aren’t sure how to spot them. Start there.
Small business cybersecurity isn’t about buying the most expensive tools on the shelf. It’s about understanding how attackers actually get in, then closing entry points before they can use them.
The good news? The same attacks tend to show up again and again. So once you can see the pattern, most attacks are easily preventable.
This guide is your map, here to walk you through why hackers go after small to medium-sized businesses, how they get in, what it costs when they win, and how to prevent them from getting access in the first place. And if you want to go deeper on any one topic, explore the links throughout.
Why Do Hackers Target Small Businesses?
Attackers target small businesses on purpose, not by accident. The old idea that you’re “too small to matter” is exactly what makes small companies easy for threat actors to hit. If you assume you’re not a target, you tend to skip the basics, which is exactly what attackers count on.
Criminals run automated tools that knock on millions of doors at once, finding vulnerabilities. A small business with light defenses (such as no MFA) and real money in the bank is a better return on their time than a hardened enterprise. Cybercrime runs like a business, and this is a business of volume.
The human side is where they win. Verizon’s annual breach research found that roughly 60 percent of breaches involve a person doing something the attacker wanted, like clicking a link or handing over a password. You can’t patch those vulnerabilities with software. But you can help prevent them with training and better habits.
How Do Hackers Actually Get In?
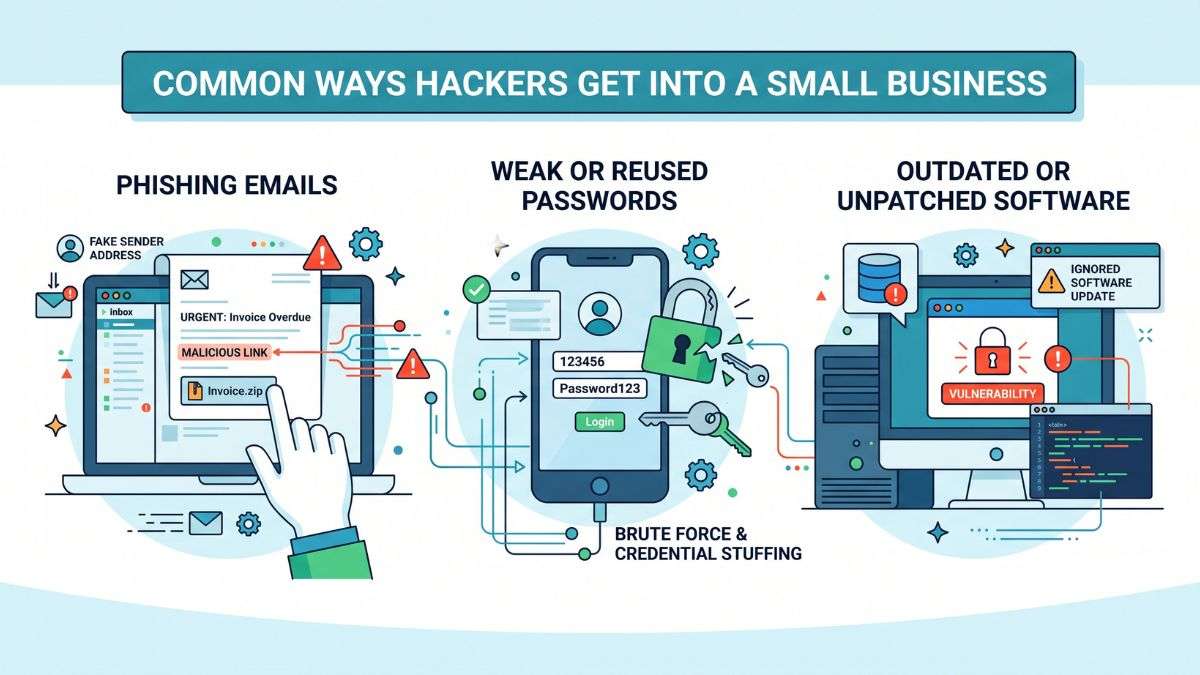
Most attacks on small businesses come through a short list of entry points, with phishing leading by a wide margin. In fact, phishing and business email fraud sit at the top of the FBI’s Internet Crime Complaint Center report year after year. The tools change, but the entry points stay the same.
Those aren’t the only entry points, though. Here are the top ways hackers breach small to medium-sized businesses, along with what each one looks like and what stops them from getting in.
| Entry Point | How It Works | What Stops It |
|---|---|---|
| Fake messages | A convincing email, text, or call gets someone to click, log in, or pay | Training and a habit of verifying before acting. Learn to spot a phishing email |
| Stolen or reused passwords | One leaked password opens several accounts | Unique passwords and multi-factor authentication |
| Out-of-date software | Old apps and systems have known holes attackers scan for | Regular updates, also called patching (this is your sign to stop procrastinating the update on your phone or computer) |
| Bad attachments and downloads | A file installs malware or ransomware when opened | Email filtering, and not opening anything unexpected |
| Lost or open devices | A missing laptop or an unsecured phone becomes a way in | Screen locks, encryption, and remote wipe |
Notice the common thread? Nearly every one of these attacks depends on a human rather than a machine. That’s called social engineering: the art of granting access. Attackers study how to gather your personal information first, then use it to make the message feel real. CISA, the federal cybersecurity agency, has said for years that most successful attacks start with a phishing message.
And these aren’t typically long, drawn-out attacks. That same breach research revealed that the median time for someone to fall for a phishing email is under a minute. These attacks work fast, which is why fixing the problem starts with changing habits, making sure team members think twice before taking a knee-jerk reaction, like clicking an email link.
What Happens After a Hacker Gets In?
A breach is rarely limited to one bad day. It’s usually a chain of them. First comes the immediate problem, like a fraudulent wire transfer or a locked system. Then, after you’ve stopped the threat at the source, you still have the cleanup: downtime, recovery costs, and the slow work of figuring out what exactly the attacker touched.
The stolen data has a long tail too. Logins, customer records, and financial details get sold and reused for the next scam, which is exactly what hackers can do with your data once they have it. For a small or medium-sized business, one click could cost you everything.
Ransomware is the version most owners fear, and for good reason. It locks up your files and demands payment to give them back. In Verizon’s latest report, ransomware showed up in roughly four out of ten breaches, up sharply from the year before. Paying the ransom is a gamble, and even then you may not get everything back. The dependable way out is backups you can actually restore from.
Picture a small accounting firm the week before a filing deadline. One fake invoice email, one click, and the files are encrypted. Firms with good backups lose hours. Firms without them lose a lot more.
Unsure which of these entry points are currently vulnerable at your business? Stratti can help you close the gaps. To start a conversation, get in touch or call (530) 342-8999.
How to Stop It: A Practical Small Business Security Checklist
You don’t need an enterprise budget to be a hard target. Security works in layers, and each layer you add makes you less appealing to an attacker. Here are some easy tips that can make a major difference in your business’s cybersecurity.
- Train your team, and keep training them. People are the target, so people are the defense. Regular, short lessons (plus the occasional practice phishing email) beat one long annual seminar. There are nine types of security training worth knowing, and most businesses do only one or two.
- Turn on multi-factor authentication everywhere it’s offered. This is the extra code or prompt after your password. It means a stolen password alone isn’t enough for threat actors to get in. It’s the cheapest, highest-return step you can take, so turn it on for email and banking first.
- Use unique passwords and a password manager. Reusing one password across accounts is how a single leak becomes five break-ins. A password manager makes strong, unique passwords painless.
- Keep everything updated. Those update reminders close the exact security holes attackers look for. Turn on automatic updates so they happen without a second thought.
- Back up your data and make sure you can restore it. A backup you have never tested is a guess. Confirm a backup ran this week, then actually restore a file to prove it works.
- Lock down phones and laptops. Require screen locks, turn on encryption, and set up remote wipe for lost devices. If your team works on the road, keep those devices secure too.
- Have a plan for when something goes wrong. Write down who to call, in what order, before you need it. A calm checklist beats a panicked group text.
| Layer | What It Protects Against | First Step This Week |
|---|---|---|
| Employee training | Phishing and social engineering | Send one practice phishing test |
| Multi-factor authentication | Stolen or guessed passwords | Turn it on for email and banking (and pretty much any other software that allows it, the more the better) |
| Password manager | Reused and weak passwords | Pick one tool and roll it out |
| Updates and patching | Known software holes | Turn on automatic updates (and install them) |
| Tested backups | Ransomware and hardware failure | Confirm a backup ran, then restore one file to make sure it works |
| Device security | Lost or stolen devices | Require screen locks and encryption |
Where Should a Small Business Start?
If you do only three things this quarter, do these: train your team, turn on multi-factor authentication, and set up tested backups. Those three stop or soften the majority of attacks hitting businesses your size. Everything else builds on that base.
Good security should feel like good plumbing. You don’t think about it, because it just works. That’s the whole point of managed IT: the layers run quietly under the hood, so your team can get back to work.
If you’re not sure where exactly your security gaps are, that’s the perfect place to start. Stratti can look at your setup, identify vulnerabilities, and help you fix weak spots in the right order. Call us in Chico at (530) 342-8999 or Roseville at (916) 290-4511, or get in touch online to get started.
Frequently Asked Questions About Small Business Cybersecurity
Small business cybersecurity is the set of habits, tools, and training a company uses to protect its data, money, and systems. In practice, it means training staff, using multi-factor authentication, keeping software updated, and backing up your data. For most small businesses, getting those basics right handles the majority of the risk.
Because small businesses are easier and still worth it. You still have money, customer data, and access worth stealing. Attackers use automated tools to find companies with weak defenses, and small businesses often have fewer security layers and no full-time security staff, which makes you a great target.
Phishing, which is a fake message that tricks someone into clicking or sharing a password. Federal cybersecurity agencies report that most successful attacks begin this way. It works because it targets people rather than technology, so the best defense is a trained team plus multi-factor authentication as a backstop.
It varies widely, but the cost is rarely just the ransom or the fraud. Add downtime, recovery labor, lost customers, and the time spent untangling what was touched. For a small to medium-sized business, the indirect costs and days of lost work often hurt more than the initial theft, which is why prevention is far cheaper than recovery.
Turn on multi-factor authentication everywhere it's offered. MFA is the extra code or prompt after your password, and it means a stolen password alone won't let an attacker in. It's also low cost, quick to set up, and blocks the most common attack path. Start with email and bank accounts.
Not fully. Those platforms give you a strong starting point, but many protections are off by default or need setup. Multi-factor authentication, safe sharing settings, and proper backups still require attention. Think of them as a good lock on the door, not the whole security system.
Ransomware is malicious software that locks your files and demands payment to release them. Most small to medium-sized businesses get hit with ransomware through a phishing email or a fraudulent download. The most reliable defense against ransomware is tested backups, so you can restore your data instead of paying, plus training to stop the click that starts it.
Short, regular training beats a single yearly session. A quick refresher every month or quarter, plus occasional practice phishing tests, keeps the lessons fresh and habits sharp. Attacks change constantly, so training that happens once and never again isn't effective for very long.
No. Antivirus is one useful layer, but it can't stop an employee from handing over a password to a convincing bad actor. Real protection combines trained people, multi-factor authentication, updates, backups, and email filtering. Security works in layers, and antivirus is only one of them.
Warning signs include logins from strange locations, coworkers reporting emails you never sent, files you can't open, or unexpected account changes. Attackers often stay hidden for weeks, so quiet doesn't always mean safe. If something feels off, treat it as urgent and bring in your IT team right away. You can also report scams and fraud to the FTC at ReportFraud.ftc.gov.
|
BL
|
Written by Brent Largent
Managed IT Services Expert · Stratti
Brent and the Stratti team have spent over three decades helping small and mid-sized businesses across Chico, Roseville, and the greater Sacramento area handle cybersecurity threats, managed IT, and technology strategy. When IT works, you don’t notice it, and that’s exactly how they like it. Last reviewed: July 21, 2026
|
