Are you a target for hackers? No matter who you are, the answer is yes. Cybercriminals rarely pick specific victims. Instead, they look for easy openings, weak passwords, accounts without multi-factor authentication, and unpatched software. Then they go after whoever fits the bill. That means every business is a target, including small and medium-sized ones. The upside? A few basic habits can help you go from an easy target to one that probably is not worth a hacker’s time.
You’re a target for hackers whether you feel like one or not, and it is not because a team of supervillains has carefully chosen your business as their next victim and pinned your headshot to their corkboard so they never lose sight of their goal. In reality, attackers choose their targets based on one factor: easy openings. If your business has a weak spot, you are worth their time, no matter how small you are.
Oftentimes, recognizing you are a target is the first step in strengthening your small to medium-sized business cybersecurity. So let us start with the three biggest questions: what hackers actually look like, why you are a target, and what you can do about it.
What hackers actually look like
When you hear the word “hacker,” you probably picture a hooded figure in a dark basement, lit only by the dim glow of their computer screen as they furiously type away to create some complex code. Today, those characters pretty much only exist in movies. Modern cybercrime is an organized industry with offices, payroll, and even performance bonuses tied to ransomware payouts.
The motive is almost always the same: money. The large majority of attacks are financially motivated, according to Verizon’s annual breach report. Criminals either want cash directly (think: “wire me money, or I will erase all your files”), or they want personally identifiable information they can use to access bank accounts (like the answers to your security questions) or resell to other criminals (because if they cannot use your data to get money, someone else will). Since collecting data is an easy way to turn a profit, what hackers can do with your personal data is exactly why businesses of every size become a target at some point.
Why are you a target?
Too often, businesses think they are not big enough, not profitable enough, or not important enough for cybercriminals to want to bother with. But to attackers, those reasons are precisely what puts them at the top of their list. Attackers love a target who thinks they do not need cybersecurity protections in place.
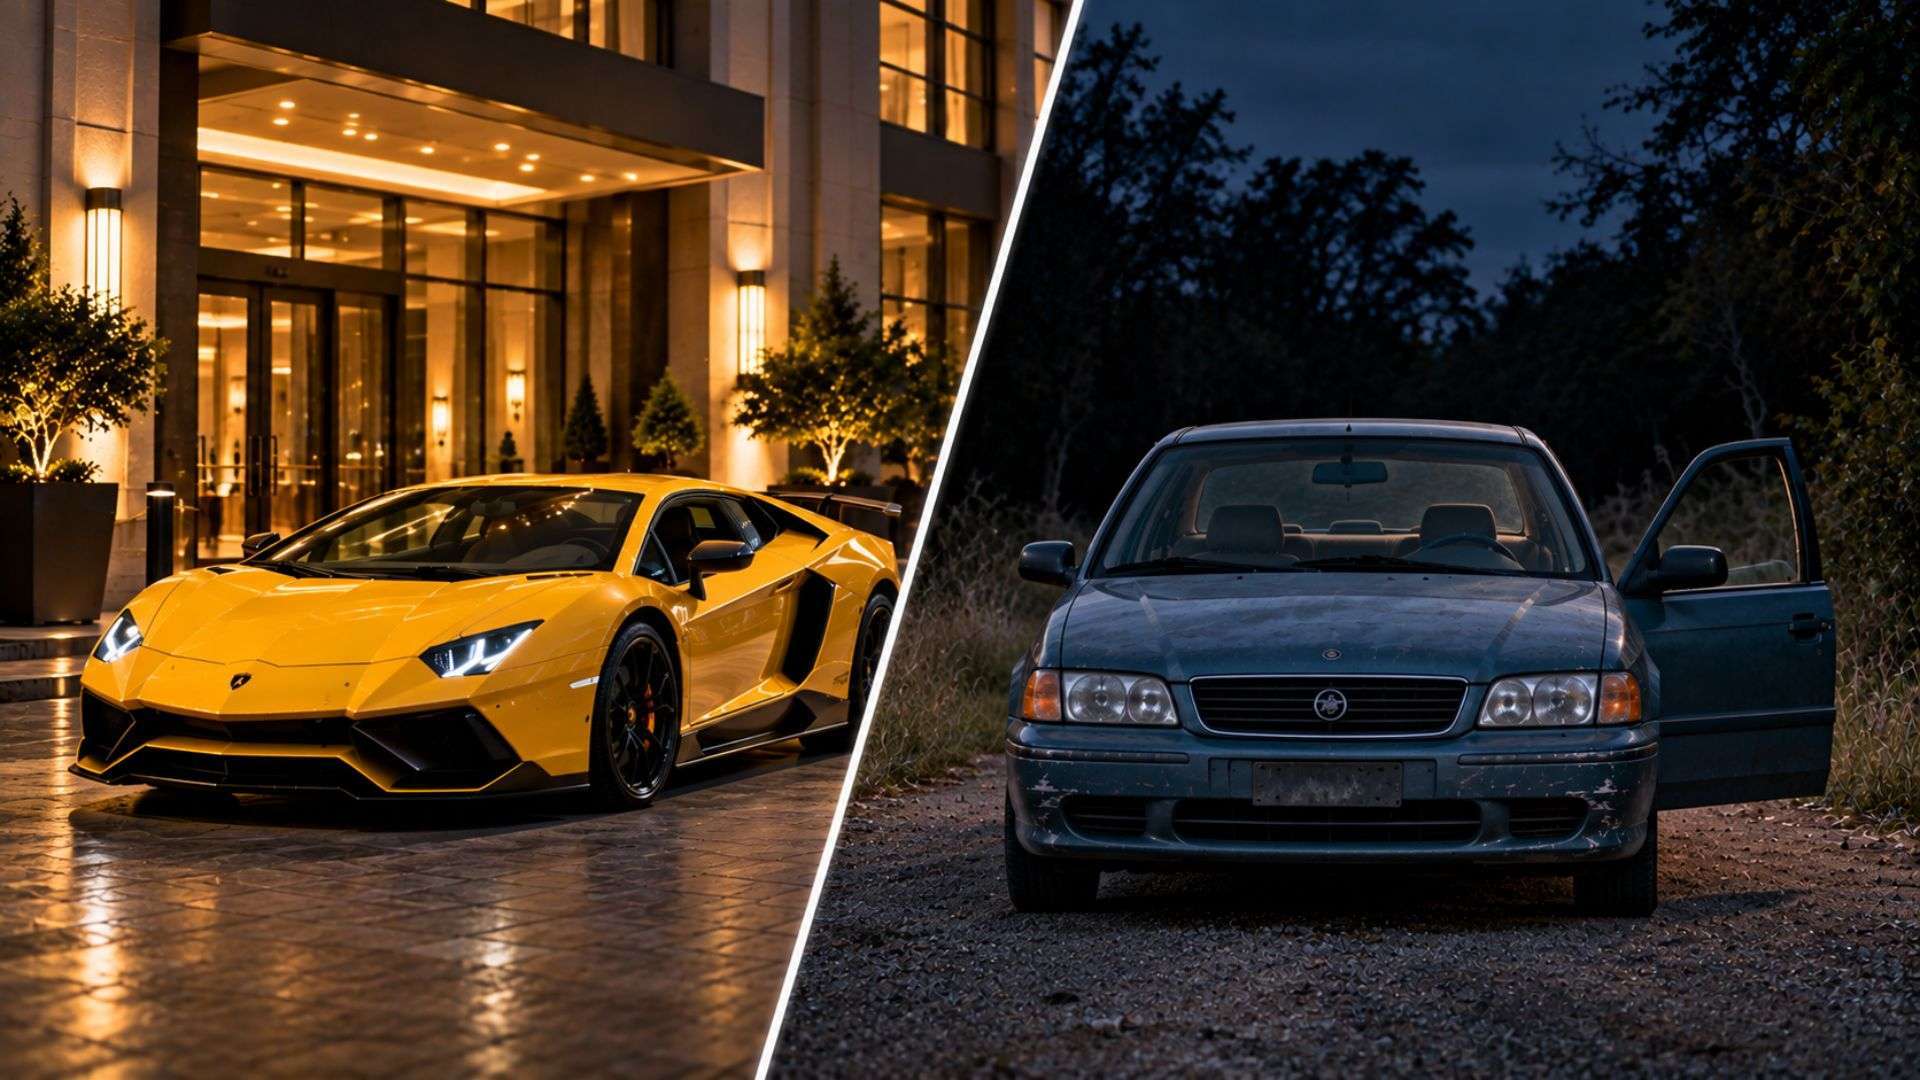
Think about it this way: when a thief wants to steal a car, they rarely go for the Lamborghini parked outside the five-star hotel. Why? Because they know the owners know they have something worth stealing, and they have likely put the right protections in place to make sure it does not happen. Instead, they find the older sedan parked on a back road with the door left open. And once they spot the vulnerability, they are driving away with it in seconds.
Cybercriminals use the same logic when they go after personal information: higher-value targets are typically better protected and riskier to hit, but a door left open by someone who does not think they are a target at all is an easy win.
They do not care who you are or what industry you are in; they care about finding weak or reused passwords, accounts without multi-factor authentication, and team members who are likely to click a link without realizing the email is not actually from their boss. They scan the whole internet for the digital equivalent of an open door, then break in through anything they can find.
What makes you an easy target?
Almost every break-in can be traced back to a short list of common weak spots. The bad news is that a lot of companies have at least one. The great news is that all of them are fixable. Here is what to look for:
- Unpatched software. Operating systems, browsers, and plugins waiting for you to finally stop hitting the snooze button on the latest update leave known security holes wide open for criminals to crawl in through. In fact, many updates are not even for new features you will notice, they are created specifically to close a security gap.
- Weak or reused passwords. Using “Admin123” across ten different accounts is a gift to an attacker. One stolen login (or a not-so-lucky guess) can have them catfishing as you in no time.
- No multi-factor authentication. The security code you have to wait for and type in after entering your password may seem annoying. But without this second step, a single stolen or guessed password is all it takes for criminals to get access to your account. Multi-factor authentication is the easiest (and cheapest) way you can help keep them out.
- Unsecured networks and devices. Connecting to open public Wi-Fi, leaving your devices behind (or worse: wide open), and using legacy software are basically the hacker equivalent of finding $20 in your old coat pocket. They are a nice, surprising way to get a quick buck, or in a cybercriminal’s case, lots of bucks.
At a glance: the most common weak spots and how to close them
| Weak spot | Why hackers love it | How to close it |
|---|---|---|
| Unpatched software | Known holes with ready-made exploits | Turn on automatic updates, and make sure they actually install |
| Weak or reused passwords | Easy to guess or reuse across sites | Strong, unique passwords stored in a password manager |
| No multi-factor authentication | A stolen password is enough to get into an account | Turn on multi-factor authentication everywhere it is offered |
| Unsecured networks and devices | An easy, quiet way into your devices and information | Use secure Wi-Fi, keep track of all devices, retire old devices and software |
How to make yourself less of a target
There is only one guaranteed way to never get hacked: go completely off-grid. Cancel every subscription, wipe your laptop and phone and throw them in a lake, and start living in a tent far away from anything with Wi-Fi.
If that sounds unreasonable (and unfair to those poor lake fish), now you know why most people choose to go the less extreme route: adding layers of cybersecurity to make your business a more difficult target.
Just like motion lights, security cameras, alarms, and locked doors make your house one burglars are more likely to skip, there are several strategies you can use to make your business less appealing to cyberattackers. Here is where to start:
- Patch and update. Turn on automatic updates for your operating systems, browsers, and software (and actually make sure they install) to keep criminals from exploiting known technical vulnerabilities.
- Use strong, unique passwords. Adding “1” to the end of your dog’s name or your favorite color will not fool hackers. Brush up on how to create a strong password, then use a password manager to keep track of them all.
- Turn on multi-factor authentication. Even when a password leaks, adding a second step to your logins blocks the large majority of account-takeover attempts. And if a hacker does try to get in, you will never be so relieved to get that “DO NOT SHARE THIS CODE WITH ANYONE” text.
- Back up your data. Tested backups you can actually restore from mean a security incident or ransomware attempt is just a bad day, not a closed business.
- Train your team. Just about every cyberattack these days starts with a human putting off a software update too long, using a weak password (again), or trusting a phishing email a little too much. Regular security training makes them a strong first line of defense, and it is the highest-return security investment you can make.
Not sure where to start? For over 30 years, Stratti has been helping businesses like yours spot vulnerabilities and patch them up before they become paydays for cybercriminals. Get in touch online or call (530) 342-8999 to get started.
Frequently Asked Questions
Yes. Most attacks are not aimed at a specific person or business. Criminals scan broadly for weak spots like unpatched software or reused passwords, shooting their shot at any business or individual who has them, no matter their size or name.
Because smaller organizations tend to have fewer defenses and no full-time security staff, so they are more likely to have a crack an attacker can slip through. If you do not think your business is big enough to be a target, you probably are not investing much in cybersecurity, which is exactly what they count on. And most of the time, attackers use automation that does not know or care how big you are.
Usually not. Research consistently shows criminals base their targets on whether a business has weaknesses rather than who they are or what industry they are in. They look for the digital equivalent of an open door: a weak password, lack of multi-factor authentication, or unpatched software. Then they walk through whatever holes they can find.
There are a few common weak spots attackers look for: unpatched software, weak or reused passwords, no multi-factor authentication, and unsecured networks or devices. The good news? Every one of these is fixable. And as soon as you fix them, you become a less appealing target.
Gone are the days of hooded figures in a dark basement. Modern cybercrime is a huge, organized industry, complete with offices, employees, salaries, and bonuses. The large majority of attacks are financially motivated, run by teams looking to make their business some cash.
No. Even if you feel you have nothing worth stealing, your accounts, customer data, and systems are all valuable to a criminal. Attackers can resell breached personal information, hijack accounts, lock down your data for ransom, or use your business to run more convincing scams on others.
Every layer of cybersecurity you add makes you less appealing to hackers. Start with the basics: turn on automatic updates (and make sure they install), use strong and unique passwords every single time, turn on multi-factor authentication everywhere it is offered, back up your data and make sure the backups work, and train your team to do the same.
The easiest and most cost-effective ways to get started are turning on multi-factor authentication and automatic updates. Then change all weak or reused passwords to strong, unique ones (a password manager can help you keep track of them all). From there, add tested backups and regular staff training.
Make yourself the business hackers skip. If you want an extra set of eyes and hands to help you lock down the basics, Stratti is available anytime to assess where you are most exposed and build a plan to help keep your business safer. Get in touch online or call (530) 342-8999 to get started.
|
BL
|
Written by Brent Largent
Managed IT Services Expert · Stratti
Brent and the Stratti team have spent over three decades helping small and mid-sized businesses across Chico, Roseville, and the greater Sacramento area handle cybersecurity threats, managed IT, and technology strategy. When IT works, you don’t notice it, and that’s exactly how they like it. Last reviewed: September 18, 2026
|
