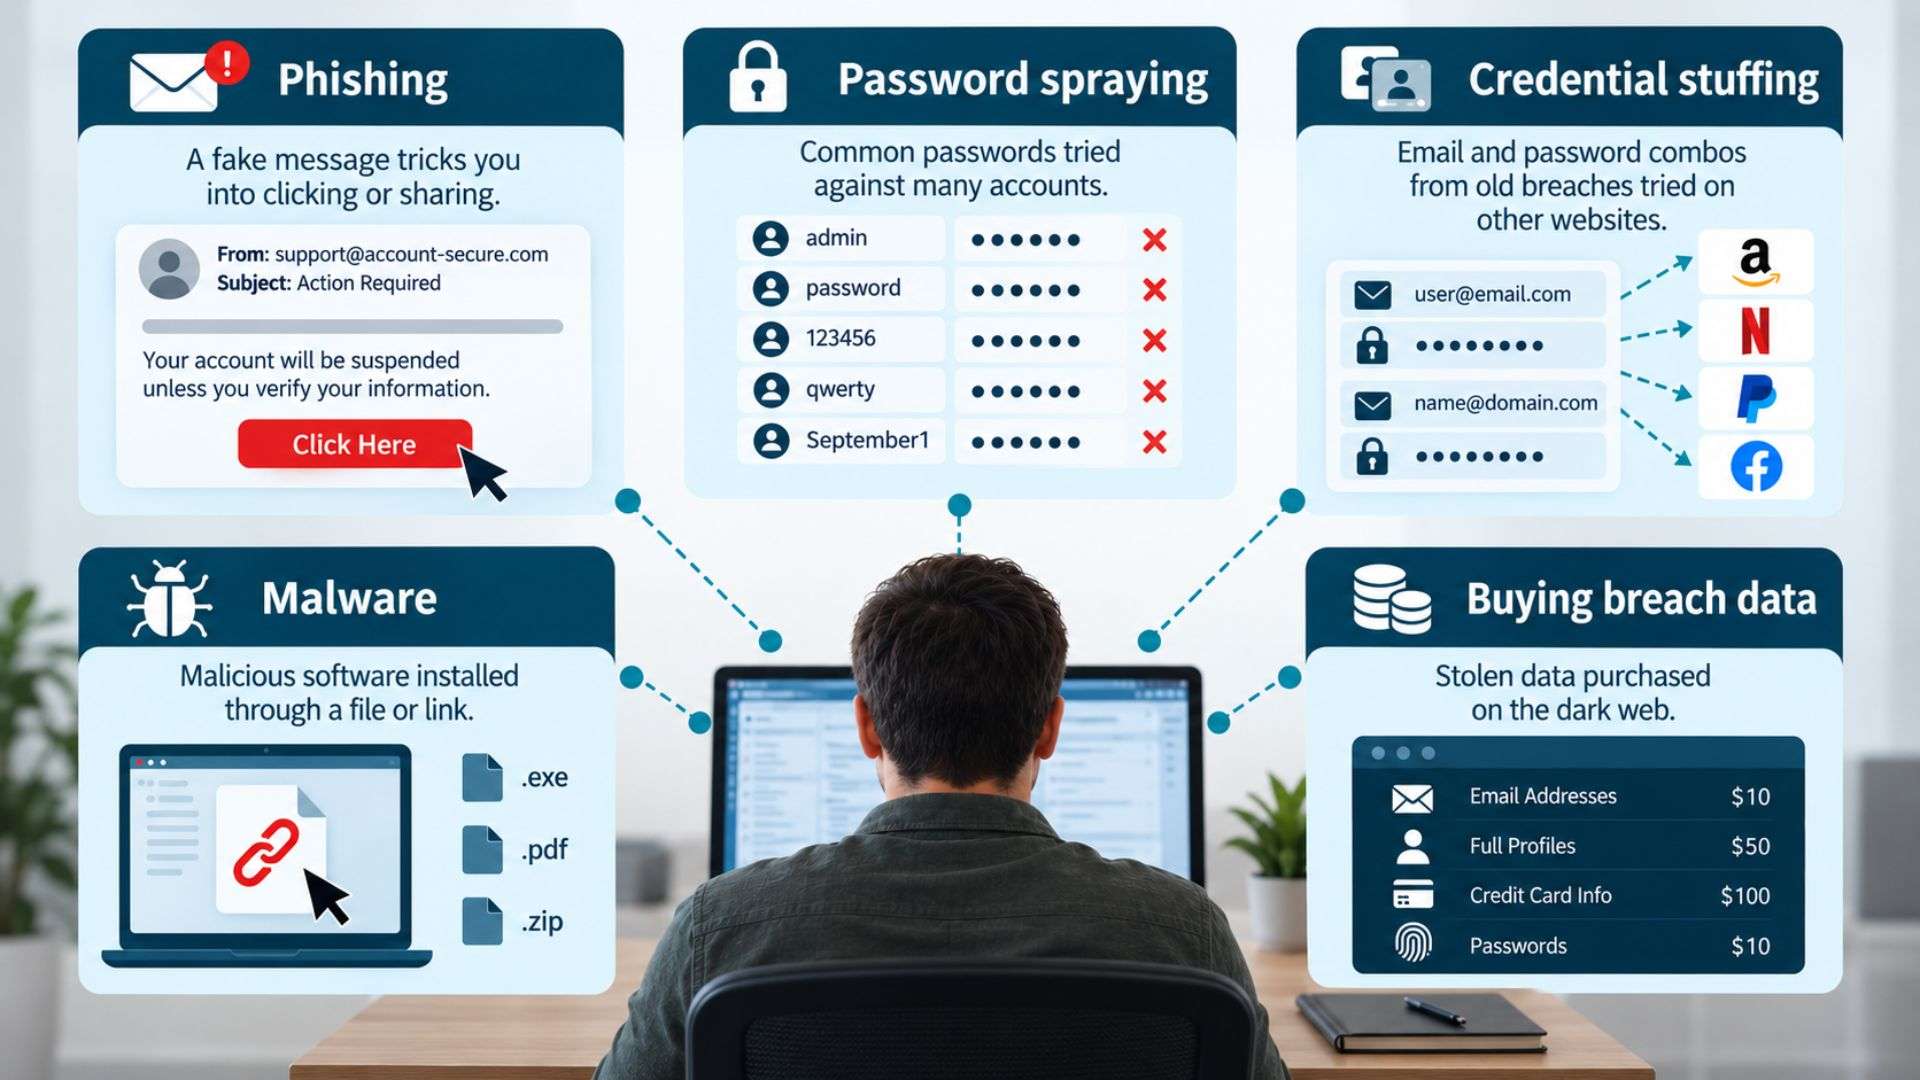
How do hackers get your personal information? Mostly through a handful of proven methods: phishing messages, password attacks like spraying (trying one or two common passwords across thousands of accounts) and credential stuffing (trying previously breached credentials across multiple websites), malware, and buying data from past breaches on the dark web. Almost all of it targets humans and weak passwords, which are two things firewalls just cannot protect.
How hackers get personal information is not the result of some hyper-detailed scheme run by mysterious hooded figures. Most of the time, they just use the same boring methods, over and over, because those methods keep working. The good news is that once you know their playbook, it is easier to remove yourself from their game altogether.
If you know anything about cybersecurity for small to medium-sized businesses, you know attackers tend to target the companies likely to have the fewest layers of protection. (And if you could use a reminder, explore the basics of small business cybersecurity to learn how to defend against them.)
Through every stolen password and successful social engineering scheme, one theme keeps coming up again and again: most breaches involve a person, not just a machine. In fact, Verizon’s annual breach report links humans to the large majority of incidents, year after year. It is why attackers continue to send those convincing phishing emails offering you a flexible remote job or telling you your package could not be delivered: they continue to work.
What personal information are hackers after?
Anything that helps them pretend to be you or access your money: Social Security numbers, bank accounts, credit card details, and username and password combos are usually targeted first. But they also look for more seemingly harmless pieces of data, like your name, birthday, address, mother’s maiden name, and even medical records. Personally identifiable information, or PII, is extremely valuable, and hackers want it enough to steal it in bulk. And once they have it, there is no limit to what hackers can do with your personal data.
How do hackers get your personal information?
If you are picturing a dark basement, a guy in sunglasses, and endless lines of code, think again. None of the methods used today require a movie-style genius, and most run on automation and volume. Here is what modern hackers go back to again and again:
1. Phishing
Phishing is the most common method for stealing personal data by far. Here is how it works: an attacker poses as someone you trust (think: your bank, your go-to vendor for supplies, your boss, a volunteer organization, Amazon, Facebook). They email, call, or text you, and they always have a story, like an emergency or a time-sensitive issue. They ask you to click a link, open a file, or type in your password. And if you do not know what to look for, you will likely do it without thinking twice, and the scheme becomes a success. The FTC even has a guide on spotting and avoiding phishing, and a quick share with your whole team could keep your business from falling victim.
2. Password spraying
When you forget your own password, you might run down your list of commonly used passwords until you figure it out (until you get locked out, at least). Password spraying is when hackers do the opposite. Instead of guessing many passwords for one account, criminals use automation to try a few very common passwords against thousands of accounts at once. In any large group, someone is more than likely using a weak password, and it only takes one for hackers to get a foot in the door.
3. Credential stuffing
Credential stuffing relies on the human tendency to reuse passwords. Attackers take username and password pairs stolen from one breach and feed them into other sites automatically, betting that people are using the exact same pair in more than one place. Spoiler alert: they often do. And suddenly, one old breach gives hackers access to several of your accounts.
4. Malware
Malware is malicious software hackers trick you into installing on your device by sending you a fraudulent attachment, download, or link. Once you click it and it starts running, it can quietly record what you type, access your camera, copy your files, steal your passwords, or hand control of your system to an attacker. Sometimes, they go a step further with ransomware: locking your files down and demanding payment in exchange for their release (and even then, there is no guarantee they will hold up their end of the bargain, since they are criminals, after all).
5. Buying it from past breaches
Sometimes the hackers targeting your business do not actually steal your data at all; they buy it. Huge lists of logins, Social Security numbers, and credit card details from earlier breaches are traded on the dark web every single day, and they are surprisingly affordable (but do not get any ideas). So if your information was ever exposed anywhere, assume it is still out there and will be reused in the future.
At a glance: how hackers get personal information and how to stop them from getting yours
| Method | How it works | Best prevention |
|---|---|---|
| Phishing | A fake message tricks you into clicking or sharing | Train the team, verify before acting, use email filtering |
| Password spraying | Common passwords tried against many accounts | Strong, unique passwords, multi-factor authentication |
| Credential stuffing | Email and password combos from old breaches tried on other websites | Never reuse passwords, use a password manager to keep track of them all |
| Malware | Malicious software installed through a file or link | Do not open anything unexpected, stay up to date on software updates, use endpoint protection |
| Buying breach data | Stolen data purchased on the dark web | Assume your info is out there, keep an eye on your accounts, change passwords frequently |
How to protect your business
Making your business impossible to target is, well, impossible. But you can make yourself less appealing to hackers. Cybersecurity works in layers, and each one you add closes a door the most common methods rely on. Here is where to start:
- Train your team. Since most attacks target a human, regular training for everyday employees is the highest-return security investment you can make. There are nine types of security training small to medium-sized businesses should look into.
- Turn on multi-factor authentication. A stolen or sprayed password is far less useful when logging in requires a second step, like a code sent to your phone or a link in your email. In fact, multi-factor authentication blocks most account-takeover attempts altogether.
- Use strong, unique passwords. Reused passwords are what make credential stuffing a successful method. A password manager full of strong, unique passwords up to snuff with the current password guidance from NIST fixes most of the risk.
- Keep software patched. Malware often rides in through security holes updates would have closed. Turn on automatic updates where you can, and make sure they are installed.
- Back up your data. If a bad actor does get their foot in the door, backups you have tested and can actually restore from are what will get you running again (without paying anyone).
Not sure where your gaps are? Stratti can help you find the weak spots attackers look for and build a plan to strengthen them before they become a problem. Get in touch online or call (530) 342-8999 to get started.
What to do if hackers already have your information
If you think an account or system is already compromised, every minute matters. The faster you can stop the bleeding, the less damage you will have to clean up afterwards. Here is your immediate gameplan:
- Change your passwords now, starting with email and financial accounts. Make sure they are strong (no pet names or common phrases) and you have not used them on any other platform.
- Turn on multi-factor authentication everywhere it is offered. Make sure a stolen password is not enough to get access to anything.
- Watch your accounts. Look for unrecognized logins, unauthorized charges, unfamiliar activity, or password resets you did not request.
- Get help fast. If a business system is involved, loop in your IT team right away so they can determine how the breach happened and make sure it does not happen again. If you are not sure who to call, call Stratti at (530) 342-8999.
Frequently Asked Questions
Hackers most commonly get your personal information through phishing messages, password attacks like spraying and credential stuffing, malware, and buying data from earlier breaches on the dark web. Almost every method skips trying to break through your firewall and instead targets humans, weak and reused passwords, or both.
Phishing. A fake email, text, or call designed to look like it is from a person or business you trust is the number one way attackers get people to accidentally share their passwords or click a malicious link. It works because it targets human trust, bypassing ironclad security software entirely.
Password spraying tries a few common passwords across many accounts, hoping someone used a weak one (and someone usually did). Credential stuffing takes real username and password pairs stolen from one breach and tries them on other sites, betting people use the same logins elsewhere (and they usually do). Both are automated, and both can be prevented by using strong, unique passwords, every single time.
Yes. If a company you did business with gets breached, your data can end up for sale no matter how careful you are. It is just another reason to have multiple layers of security: strong, unique passwords, multi-factor authentication, and monitoring your accounts, so one exposed detail is the only one they get.
They use it to steal identities, open credit accounts, drain your money, and run more convincing scams. It is a lot easier to believe a phone call is really from your bank when the caller knows your name, address, email, and the last four digits of your account. And after they are done, they resell it to other criminals. Get the full breakdown of what hackers can do with your personal data.
Watch for new accounts you did not open, charges you did not authorize, and password-reset emails you did not request. Checking your credit report and account activity regularly helps you catch any suspicious activity early. Keep an eye out for publicly reported breaches as well, in case a company that has your data becomes a victim.
Create as many layers of defense as possible. Train your team, turn on multi-factor authentication, use strong and unique passwords, keep software patched, back up your data, and test those backups to make sure they work. Every step you take makes the most common hacking methods less likely to work on you.
No. Actually, smaller organizations are often ideal targets for hackers because they tend to have fewer security layers and no full-time security staff. Plus, hackers use automation to carry out most attacks, and automation does not know or care how big you are. And that makes everyone a target.
Close security holes before hackers find them. If you are not sure where to start, Get in touch or call (530) 342-8999 to start a conversation about safer personal information.
|
BL
|
Written by Brent Largent
Managed IT Services Expert · Stratti
Brent and the Stratti team have spent over three decades helping small and mid-sized businesses across Chico, Roseville, and the greater Sacramento area handle cybersecurity threats, managed IT, and technology strategy. When IT works, you don’t notice it, and that’s exactly how they like it. Last reviewed: September 18, 2026
|
